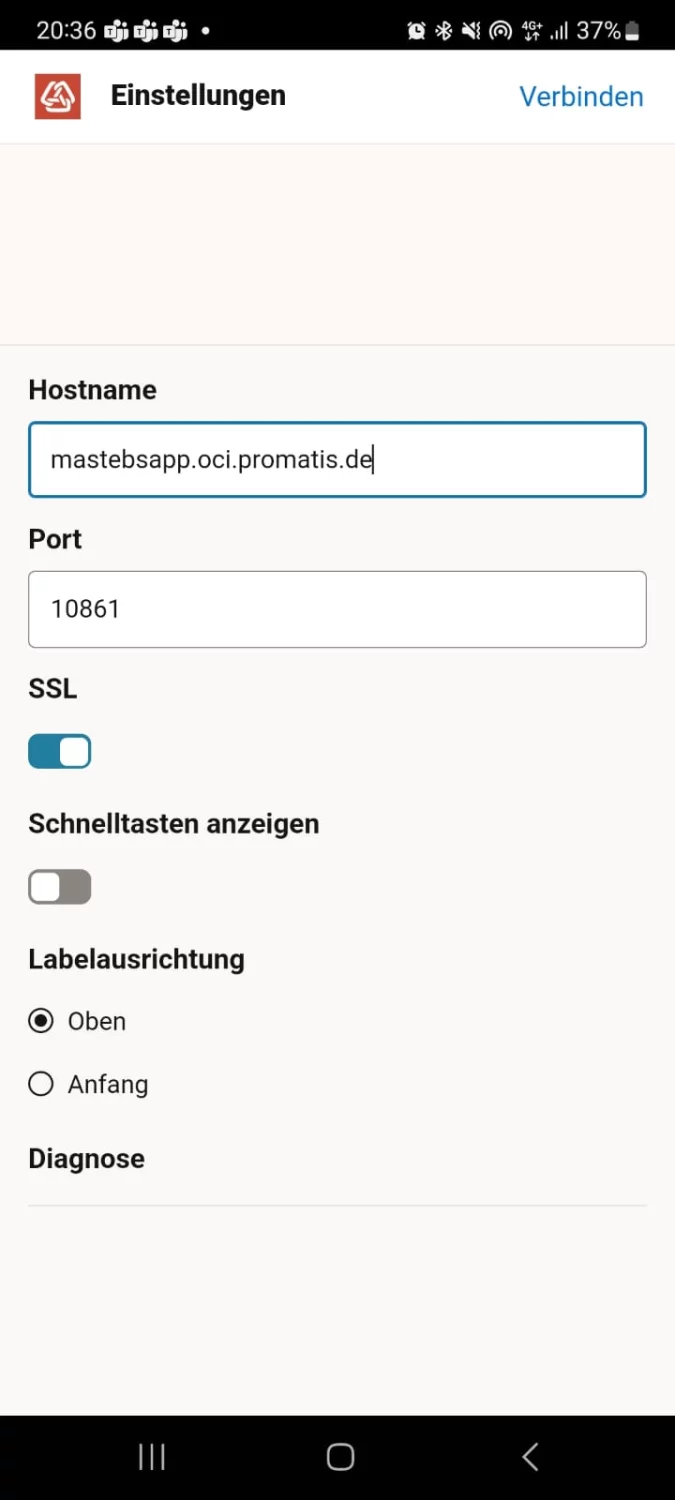
Oracle Mobile Supply Chain Application Apps (MSCA) / Mobile Web Applications (MWA) rely on a telnet-style protocol to connect from the client - be it an Android or iOS device or be it a dedicated scanning hardware - to the application server.
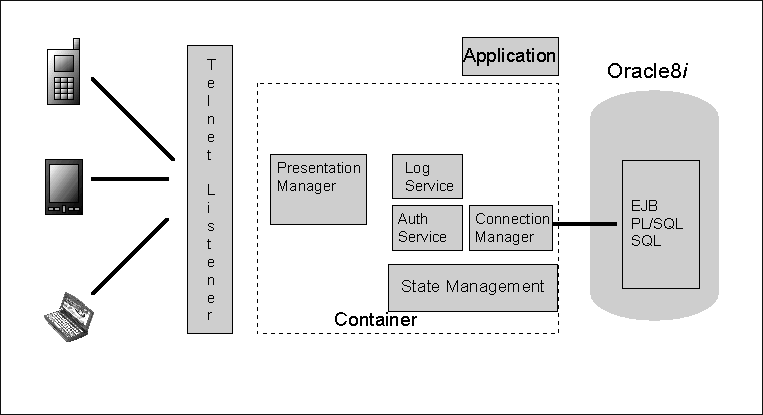
Oracle MSCA/MWA architecture, see https://docs.oracle.com/cd/E26401_01/doc.122/e48826/T256582T257759.htm
I've seen many customers that rely on unencrypted traffic from the mobile devices to the telnet server running as part of Oracle E-Business Suite 12.2. Nowadays, this is no longer state-of-the-art as well as a severe security risk. Fortunately, for quite some time now, MWA/MSCA can be run in a way to run through an encrypted TLS tunnel. This is documented in 2108155.1.
Unfortunately, the process to set this up as described in the note is not trivial, especially since it means there is another place where SSL certificate/keys need to be maintained. Furthermore, with this approach, it is no longer possible to use the MWA dispatcher to dispatch between multiple telnet servers (2175344.1).
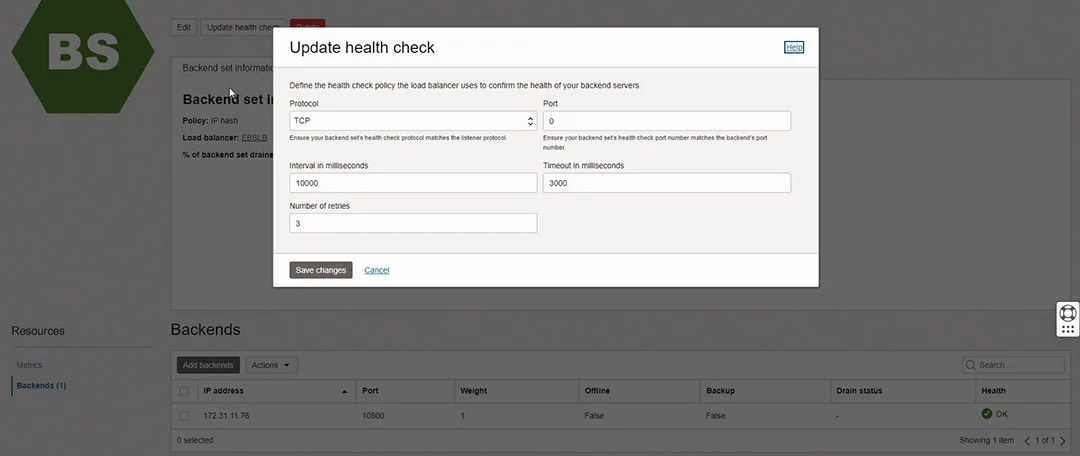
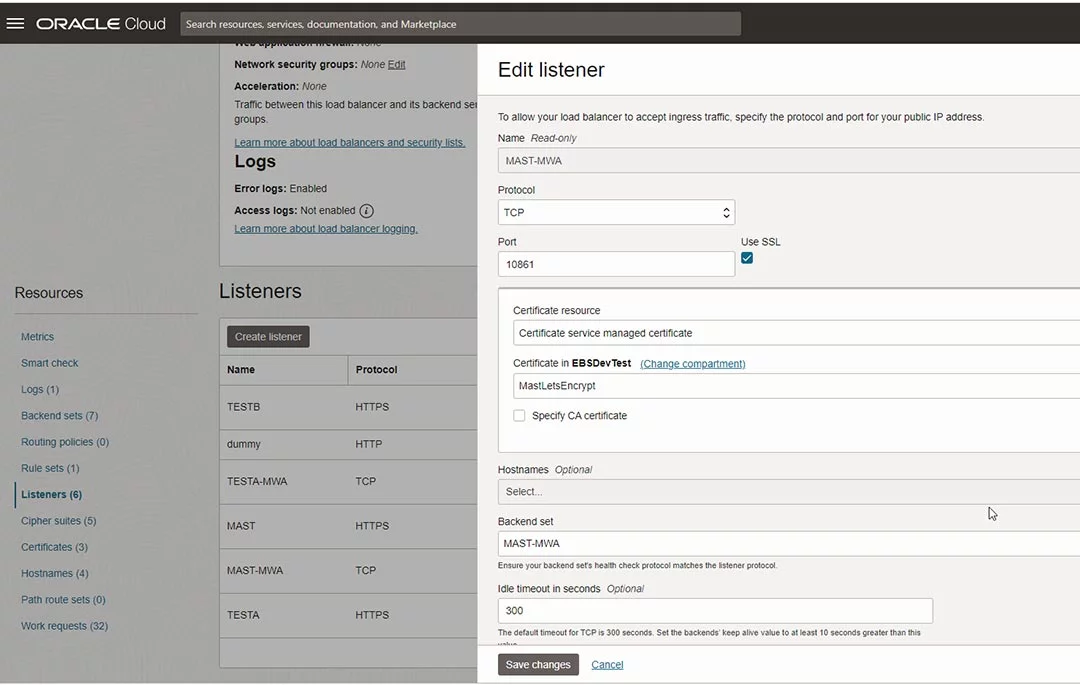
For a recent project, we thus decided to terminate TLS at a load balancer on OCI instead of at the MWA application server itself. That gives us encrypted connections through (potentially) less secure networks from the mobile device to the OCI Load Balancer - e.g. even using let's encrypt certifcates as described here: Oracle OCI Load Balancer with Lets Encrypt (free) SSL certificates. And on the E-Business Suite side, it requires no additional setup compared to a non-encrypted setup. Let's see how we managed to achieve this.